The short version
- People can catch some scam websites from obvious visual mistakes, but appearance alone is not a reliable detector.
- Controlled phishing studies have repeatedly found substantial error rates even when participants know they are being tested for fraud.
- Polished design can increase perceived credibility, which means professional presentation can work in a scammer’s favour rather than against them.
- The stronger checks happen outside the page design: verify the actual domain, how you reached the site, the organization behind it and independent records.
The short answer: not reliably
A terrible scam website can absolutely give itself away. Misspelled buttons, broken layouts, stretched logos, incoherent copy and an imitation bank page that looks ten years out of date are useful warning signs.
The problem is the reverse inference.
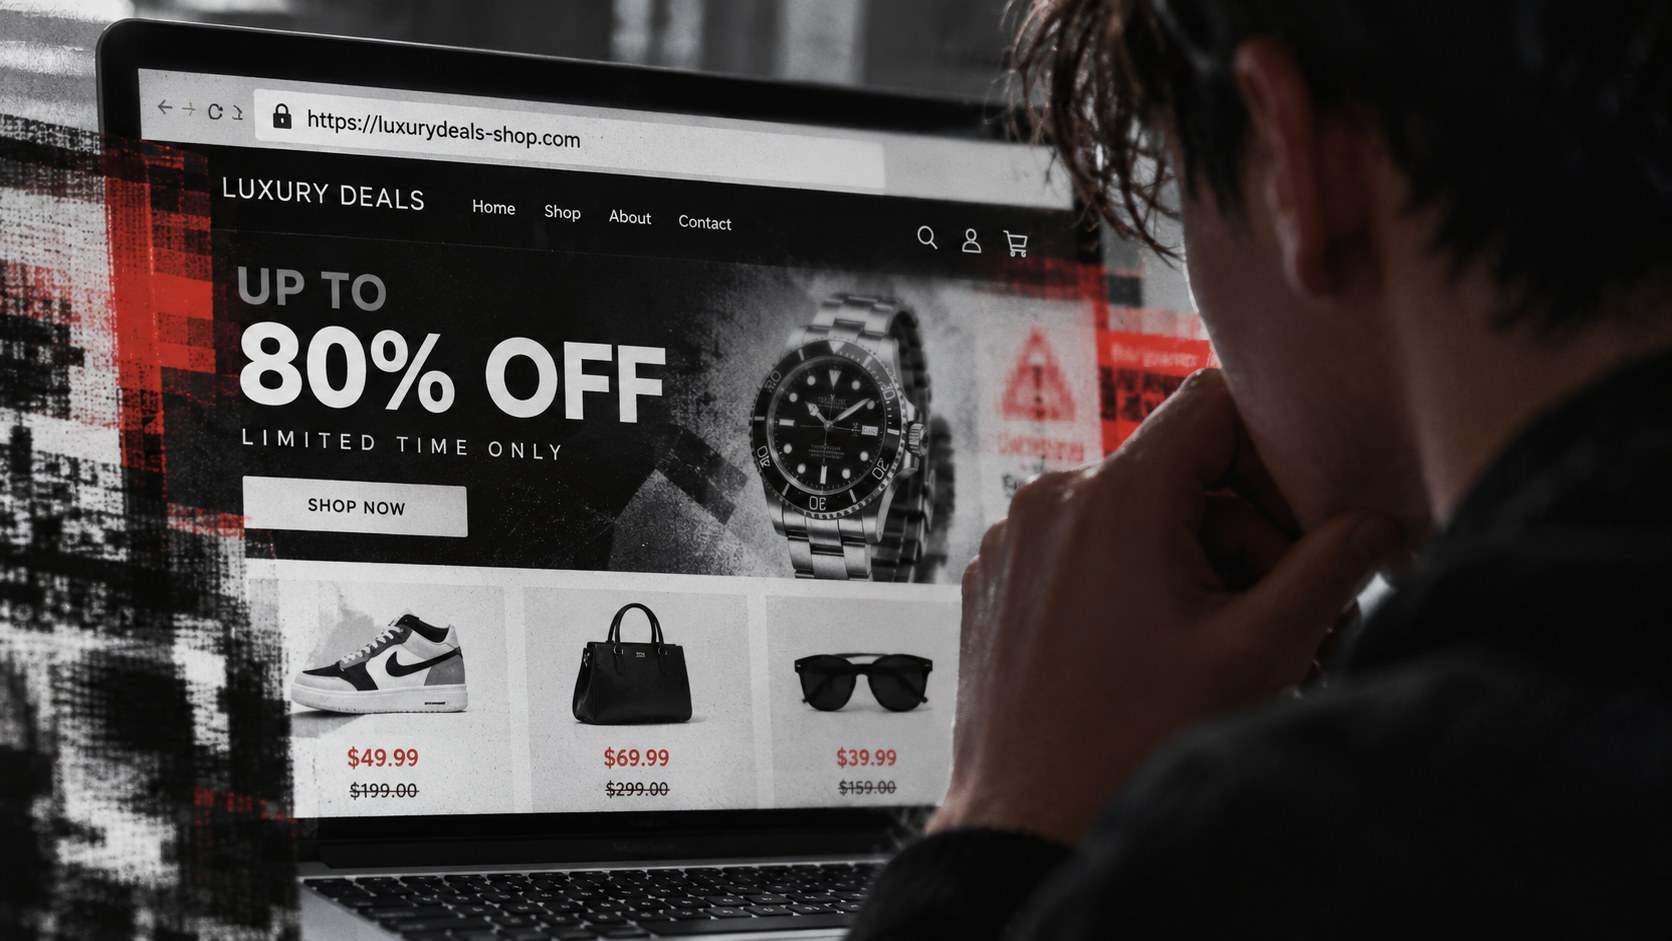
A website that does not look suspicious is not therefore legitimate. The strongest evidence from phishing research points in the opposite direction: people often rely heavily on the visible page, scammers can reproduce that visible page extremely well, and the cues that actually establish identity tend to sit outside the design itself.
That distinction matters because “scam website” covers many things. A fake store, investment scheme and credential-stealing bank clone are not the same attack. Most controlled human-subject research has focused on phishing and spoofed websites, where a fraudulent page imitates a legitimate one. The findings do not prove that every type of scam site is equally difficult to detect. They do show why judging legitimacy from appearance alone is a bad security model.
People miss convincing fakes even when they are looking for them
One of the classic experiments is still unusually direct.
In the 2006 CHI paper Why Phishing Works, Rachna Dhamija, J. D. Tygar and Marti Hearst showed 22 participants 20 websites and asked them to decide which were fraudulent. Participants made mistakes on 40% of the test set on average. Twenty-three percent did not use browser-level cues such as the address bar, status bar or security indicators. The researchers reported that their most effective phishing site fooled about 90% of participants.
That study used the web of 2006, so its exact percentages should not be treated as a current population estimate. The underlying problem did not disappear with cleaner browsers and greater public awareness.
A 2015 eye-tracking study, Why phishing still works, again asked people to classify websites while researchers measured where they looked. Participants detected only 53% of the phishing sites even though the task explicitly primed them to look for phishing. They spent relatively little time looking at browser security indicators compared with page content. More attention to browser chrome was associated with better detection.
A later simulated web-surfing experiment reported 64% overall threat-detection accuracy. Spoofed sites were harder: participants correctly identified them 49% of the time, compared with 69% for non-spoof sites.
The exact tasks, samples and websites differ, so those numbers should not be collapsed into one universal “human scam-detection rate.” They do agree on something more useful: a person can be alert, technically comfortable and actively searching for fraud while still being fooled by a convincing page.
A polished website can actually increase trust
There is another reason visual judgment is dangerous: aesthetics are not neutral.
In a 2008 experiment on aesthetics and website credibility, David Robins and Jason Holmes presented the same content with different levels of visual treatment. The more aesthetic version received higher credibility judgments in 19 of 21 comparisons. The researchers described this as an “amelioration effect”: better presentation improved how credible the underlying information felt.
That does not mean attractive websites are suspicious. It means attractiveness is capable of moving the credibility judgment even when the underlying content has not changed.
The effect begins quickly. Research on website first impressions has found that visual complexity and prototypicality can change aesthetic judgments after exposures measured in tens of milliseconds. Those experiments measured aesthetics, not scam detection, so they should not be stretched into a fraud result. They help explain why the first feeling arrives so early: a page can look familiar, orderly and professionally built before the reader has verified anything about who operates it.
For a scammer, that is useful. Logos can be copied. Product photography can be stolen. A familiar checkout layout can be recreated. Trust badges can be pasted into a page as images. A polished template can be bought or generated far more cheaply than the legitimate business the design is meant to imply.
The page can borrow the appearance of an institution without borrowing its identity.
Which visual cues are actually useful?
Some visible signs still deserve attention. Their value is asymmetric: a bad cue may justify stopping, while a good-looking cue rarely justifies trusting.
| Visible cue | What it can tell you | What it cannot prove |
|---|---|---|
| Broken grammar, inconsistent design, low-quality images | The site may be careless, copied or fraudulent | A clean site is legitimate |
| Familiar logo, colours and layout | The page is imitating a recognizable brand language | The brand operates the domain |
| Reviews or trust badges shown on the page | The operator wants you to see social proof | The reviews, badges or ratings are authentic |
| HTTPS / an encrypted connection | Data between the browser and that domain is encrypted | The domain belongs to the company it claims to represent |
| A plausible-looking URL | The address was designed to look believable | The registrable domain is the correct one |
| Browser warning or interstitial | The browser or reputation service has detected a risk signal | The absence of a warning makes an unknown site safe |
The most important row is the URL. It is still visual information, but it is not part of the website’s own artwork. The browser controls the address bar; the page controls almost everything below it.
That makes the domain one of the few visible elements a cloned page cannot simply reproduce inside its own content.
The address bar is stronger than the page — but people still struggle with it
Checking a URL sounds easy until the fake is brand-support.com, brand.com.login-example.net, a one-character typo, or a visually similar character from another alphabet.
A 2025 USENIX Security study tested structured URL-inspection tasks with 2,673 participants. The intervention reduced successful phishing compared with the baseline and was particularly helpful with difficult typo-squatted URLs. The researchers emphasized directing attention to URL structure and matching the domain to the user’s intended destination.
That is a different strategy from asking whether the page “looks right.” It forces a small identity check:
What domain am I actually on, and is that the domain I intended to visit?
Current government guidance makes the same shift. The Canada Revenue Agency warns that fake websites can be very convincing and tells users to inspect web addresses carefully or type known official addresses directly into the browser. The U.S. Federal Trade Commission similarly warns that scammers can buy search ads and build sites that look official, recommending direct navigation when the real address is known.
The recurring lesson is simple: verify the route and identity, not the production quality.
A better 30-second check
When a site matters — because it wants a password, payment, identity document, wallet connection or sensitive information — use appearance only as the first filter.
- Read the actual domain in the address bar. Ignore the logo for a moment. Identify the registrable domain and look for added words, substitutions or unexpected endings.
- Ask how you arrived there. A link from an unsolicited message, QR code, social ad or sponsored search result deserves more scrutiny than a bookmark or address you typed yourself.
- Navigate independently when possible. Open a fresh tab and find the organization through a known address, saved bookmark, statement, card or another trusted record instead of continuing through the supplied link.
- Verify claims outside the website. Check business registration, regulator records, official contact information, independent reporting or the organization’s established channels as appropriate to the claim.
- Treat pressure as information. A page that needs you to act before you verify — “pay now,” “wallet expires,” “account closes today” — is telling you something about the transaction even if the page itself looks immaculate.
None of these checks is perfect in isolation. Together they move the decision away from “does this feel real?” and toward evidence a scammer has less control over.
Visual cues are good for suspicion, not verification
The old stereotype of a scam site — ugly, broken, full of typos — survives because those sites still exist. It is useful when the stereotype catches a lazy fraud.
It becomes dangerous when people turn it into a trust rule.
A suspicious visual cue can be enough reason to stop. A professional visual cue is not enough reason to proceed. Research on phishing shows that convincing imitations routinely survive human inspection, while research on web credibility shows that attractive presentation can itself increase perceived trust.
That is why the better question is not “Does this website look legitimate?”
It is “What evidence connects this page to the organization, seller or service it claims to be?”
The same principle applies to other forms of online proof. A screenshot may look perfectly authentic while leaving the important context outside the frame; the image is only the beginning. A website is similar. Its visible surface is evidence of what was rendered on a screen. It is not, by itself, proof of who is behind it.
Sources & reference material
- Why Phishing WorksCHI 2006 / UC eScholarship · Accessed Oct 10, 2026
Usability study of 22 participants judging 20 websites; participants made mistakes 40% of the time on average, 23% did not use browser security cues, and the strongest phishing site fooled about 90% of participants.
- Why phishing still works: User strategies for combating phishing attacksInternational Journal of Human-Computer Studies · Accessed Oct 10, 2026
Eye-tracking study finding participants detected only 53% of phishing websites even when primed to identify them; greater attention to browser chrome correlated with better detection.
- Statistical Models for Predicting Threat Detection From Human BehaviorFrontiers in Psychology · Accessed Oct 10, 2026
Simulated web-surfing study reporting 64% overall threat-detection accuracy, with spoof websites correctly identified 49% of the time versus 69% for non-spoof sites.
- Aesthetics and credibility in web site designInformation Processing & Management · Accessed Oct 10, 2026
Experiment showing that higher aesthetic treatment increased perceived credibility for the same content; credibility improved in 19 of 21 paired cases.
- The role of visual complexity and prototypicality regarding first impression of websitesInternational Journal of Human-Computer Studies / Google Research · Accessed Oct 10, 2026
Experiments showing website visual complexity and prototypicality can influence aesthetic judgments after extremely brief exposures, including 17 to 50 milliseconds.
- URL Inspection Tasks: Helping Users Detect Phishing Links in EmailsUSENIX Security 2025 · Accessed Oct 10, 2026
Online study with 2,673 participants finding structured URL-inspection tasks reduced successful phishing, with especially strong benefits for difficult typo-squatted URLs.
- Recognize a scamCanada Revenue Agency · Accessed Oct 10, 2026
Current government guidance noting that fake websites can be highly convincing and recommending verification of the web address and direct navigation to known official sites.
- Online search results: The good, the bad, and the scammyU.S. Federal Trade Commission · Accessed Oct 10, 2026
Consumer guidance warning that scammers can use paid search results and official-looking websites, and recommending direct navigation to known company or government addresses.